
Innovating Globally, Rooted in Pakistan
Follow us on Social Network
Note on Confidentiality: Due to a strict Non-Disclosure Agreement (NDA) signed with our client, we are unable to disclose their brand name or specific identifying details. This case study focuses entirely on the technical challenges encountered and the solutions architected by Zarin Solutions.
A federal government agency tasked with handling sensitive, classified civilian data needed an immediate overhaul of their network architecture to comply with new executive cybersecurity mandates and protect against state-sponsored APTs (Advanced Persistent Threats).
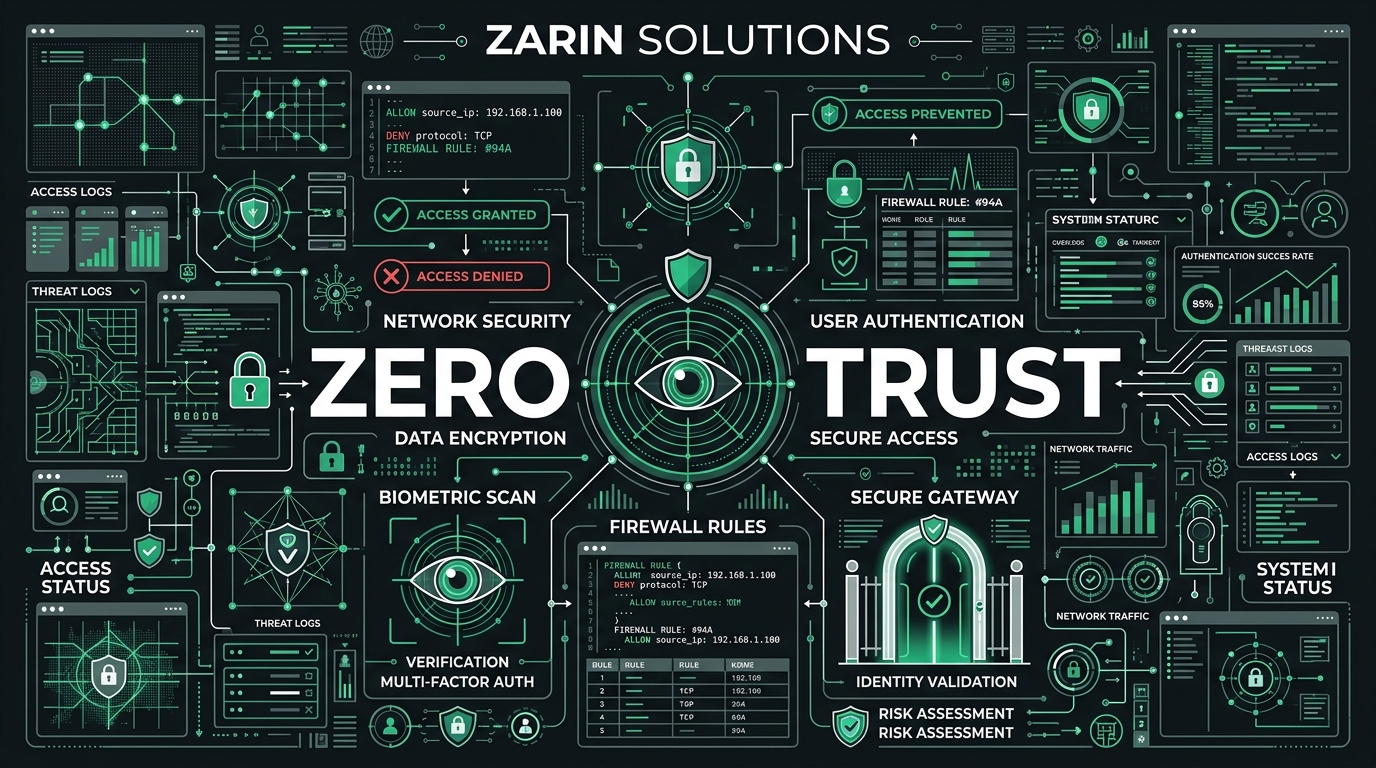
The Zarin Solutions Approach: We architected a rigorous Zero-Trust environment. We eliminated the concept of a 'trusted internal network,' implementing continuous authentication and authorization for every user, device, and application requesting access.
No Default Trust
Least Privilege Model
Automated Isolation
Government agencies often run on a complex mix of modern cloud infrastructure and decades-old legacy mainframes. The massive challenge was imposing a modern, identity-aware Zero-Trust model across these disparate, often incompatible systems without breaking critical inter-agency data flows.
We delivered a network where trust is never granted implicitly, fundamentally neutralizing the threat of lateral movement.
Users are continuously authenticated in the background based on behavior, location, and device health metrics.
Segmented the network so finely that an attacker compromising a single workstation has absolutely no path to critical databases.
Used advanced secure proxies to wrap legacy mainframes in Zero-Trust policies without needing to rewrite old code.
Integrated SOAR capabilities to automatically revoke access and isolate devices the second anomalous activity is detected.
"Zarin Solutions helped us meet stringent federal cybersecurity mandates ahead of schedule, providing a fortress-like architecture that protects our nation's most sensitive data."

